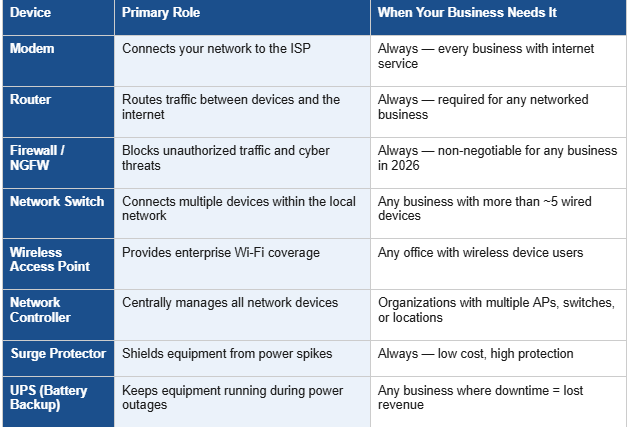
The most common network equipment for business includes: a modem (ISP connection), a business-grade router (traffic management), a firewall or next-generation firewall (security), a managed network switch (internal device connectivity), wireless access points or WAPs (Wi-Fi coverage), a network controller (centralized management), surge protectors, and a UPS (Uninterruptible Power Supply) for power protection. Together, these devices form the backbone of a reliable, secure business network.
Walk into almost any business and the network equipment is invisible — locked in a closet, humming quietly, taken for granted until it stops working. But the hardware behind your network is not interchangeable. Every piece has a specific job, and selecting the wrong equipment — or deferring replacements too long — has direct consequences for performance, security, and cost.
This guide breaks down each common piece of business network equipment in plain language: what it does, why it matters, how to recognize when you have the wrong one, and what separates consumer-grade from business-grade. For a deeper technical breakdown of each component, see our detailed guide to business network components. For a look at the financial case for upgrading aging equipment, our article on how a network upgrade can save your business money is worth reviewing alongside this one.
At Ferrara IT, we help businesses across the Philadelphia metro area and beyond select, install, and maintain the right network infrastructure — without overbuying or underbuilding. Here is what we recommend every business owner understand about their network hardware.
Before diving into each device, here is a plain-English summary of what each piece of equipment does and when your business needs it:
Translates ISP signals into usable network data — and back again
Many ISPs provide a modem or gateway device as part of the service contract. While convenient, these ISP-supplied devices are typically consumer-grade and offer limited control. Businesses with complex networking requirements — multiple internet connections, advanced routing, or strict security policies — often deploy a separate dedicated modem, giving their IT team independent control over both layers of the stack.
For simple setups, an ISP-provided modem is acceptable. However, businesses with multi-WAN connectivity, strict security requirements, or the need for full IT control often benefit from a dedicated business modem. ISP-provided modems limit configuration options, receive infrequent firmware updates, and may not integrate cleanly with business-grade routers or firewalls.
Manages every data packet moving between your internal network and the internet
Consumer routers — the kind sold at electronics retailers for home use — are not engineered for commercial workloads. They lack the throughput, security controls, and management capabilities that a business environment demands. More importantly, a consumer router placed behind a business firewall can create configuration conflicts, undermining the security controls you are paying for.
QoS is a traffic management feature built into most business routers that allows administrators to assign bandwidth priority to specific applications or device types:
Without QoS, all traffic competes equally — meaning a large file upload can degrade a live client call. In a business environment, that is not an acceptable trade-off.
Business routers are engineered for sustained concurrent user loads, advanced security policy enforcement, VPN support, and centralized management. Consumer routers are designed for light, occasional home use. In a business environment, a consumer router typically underperforms under load, lacks enterprise security controls, and conflicts with dedicated firewalls — creating security gaps rather than closing them.
Monitors, filters, and blocks unauthorized traffic at the network perimeter
A traditional firewall inspects traffic by port number and IP address. A Next-Generation Firewall (NGFW) goes significantly further — examining the actual content of network traffic, identifying applications, and actively blocking threat patterns in real time:
Leading NGFW vendors include Fortinet (FortiGate), Palo Alto Networks, Cisco (Firepower/Meraki MX), and SonicWall. For small and mid-sized businesses, managed cybersecurity services that include NGFW deployment and monitoring deliver enterprise-level protection without requiring a dedicated in-house security team.
Yes. Traditional firewalls are no longer sufficient against modern threat techniques. Attackers targeting SMBs use application-layer exploits, encrypted malware delivery, and credential theft none of which basic packet-filtering firewalls can detect. An NGFW is the correct baseline for any business handling customer data, financial transactions, or sensitive records. The cost of an NGFW is a fraction of the average cost of a data breach.
Provides centralized management of all network devices from a single interface
Without a network controller, every access point and switch must be configured individually — a time-consuming process that introduces configuration inconsistencies and makes troubleshooting far more difficult. As a business adds users, devices, or locations, centralized management shifts from convenience to operational necessity.
For businesses working with a managed IT services provider, a cloud-managed network controller is the mechanism that enables your IT partner to monitor, reconfigure, and troubleshoot your infrastructure remotely — without sending a technician on-site for every change. This is a key driver of reduced IT support costs over time.
Connects all wired devices within the local network and manages internal traffic
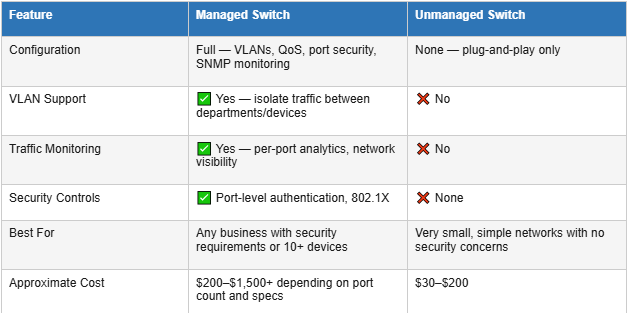
An unmanaged switch is a simple plug-and-play device with no configuration options. A managed switch gives administrators control over VLANs, traffic prioritization, port security, and network monitoring. For any business with security policies, regulatory compliance requirements, or more than a handful of devices, a managed switch is the appropriate choice.
Many business switches support Power over Ethernet (PoE), which carries both data and electrical power through the same network cable. PoE-powered devices include:
PoE+ (IEEE 802.3at, 30W per port) and PoE++ (IEEE 802.3bt, up to 90W per port) handle higher-power devices. When specifying a switch, confirm its total PoE power budget supports all connected devices simultaneously — not just the per-port maximum.
Deliver reliable, secure Wi-Fi throughout the workspace — beyond what a router antenna can provide
A router's built-in Wi-Fi antenna works for a home office. In a business environment with 10 or more employees, concurrent cloud applications, VoIP calls, and video conferences, it is simply insufficient. Dedicated access points are not an upgrade — they are the correct starting point for any business network design.
As a general rule, a single business-grade access point covers 1,500–2,500 square feet in an open-plan environment. Dense office layouts with walls, conference rooms, and 20+ concurrent wireless devices typically require one access point per 1,000–1,500 square feet. A professional wireless site survey — which maps signal propagation across your specific floor plan — gives the most accurate count before hardware is purchased.
Every piece of network equipment covered above has one shared vulnerability: power. A power surge, voltage spike, or outage can damage or destroy hardware instantly — and it happens more often than most business owners realize.
Absorb power spikes and electrical surges before they reach your hardware
Battery backup that keeps network equipment running during power events and allows safe shutdowns during extended failures
At minimum, connect your firewall, core network switch, and router to a UPS. Any on-premises server or NAS should also have UPS protection. Size your UPS based on the total wattage draw of connected devices, adding a 20–25% overhead buffer to account for efficiency loss and capacity headroom. A UPS sized too small for the load will shut down immediately under load, defeating its purpose.
The hardware covered in this guide is only part of the equation. Each device needs to be correctly selected for your environment, properly configured, and maintained over time. A business-grade firewall with default settings is not significantly more secure than having no firewall at all. A managed switch with VLANs never configured delivers the same performance as an unmanaged one.
Configuration is where the value of working with an experienced managed IT services provider becomes concrete. The hardware investment is straightforward. The expertise to design a secure, high-performance network using that hardware — and to keep it running correctly as the business changes — is the actual deliverable.
If your current network equipment is more than three to five years old, or if you are experiencing recurring performance or security issues, a professional network upgrade may deliver a faster return than continuing to repair aging hardware. Our guide to how a network upgrade can save your business money walks through the financial case in detail.
Most network equipment has a practical lifespan of 3–5 years before performance, security firmware support, or vendor patch availability becomes a concern. Firewalls and routers should be evaluated every 3–4 years for security relevance. Switches can often run 5–7 years in stable environments. Access points should be refreshed when a major Wi-Fi standard (such as Wi-Fi 6) provides meaningful throughput or density improvements for your user count.
If forced to rank them: a properly configured NGFW (firewall) is the most critical. An unprotected network is exposed to cyber threats regardless of how good the other hardware is. A business-grade router comes second — without correct traffic management, performance suffers for every user. Everything else supports those two foundational devices.
Short term, yes. Long term, no. Consumer-grade equipment underperforms under business workloads, lacks enterprise security controls, receives infrequent firmware updates, and typically carries shorter warranties. The hidden costs — increased IT support time, higher breach risk, recurring connectivity issues, and early hardware failures — consistently exceed the initial savings on hardware purchase price.
A router manages traffic between your local network and the internet — it connects your network to the outside world. A network switch manages traffic between devices within your local network — it connects computers, printers, servers, and phones to each other. Most business networks require both: a router for external connectivity and one or more switches for internal device communication.
Every business network is different. The right equipment list depends on your office size, headcount, security requirements, compliance obligations, and growth plans. What does not change is the principle: business-grade infrastructure, correctly selected and professionally configured, consistently outperforms the alternative — in performance, security, and total cost of ownership.
At Ferrara IT, our process begins with understanding your environment before recommending any hardware. We evaluate what is currently in place, identify gaps, and design infrastructure that fits your actual needs — not a one-size-fits-all template. Whether you need a complete network build-out, a targeted equipment refresh, or ongoing managed IT services to monitor and maintain your infrastructure, we bring the expertise to do it correctly.
Contact Ferrara IT today to schedule a free network assessment. We will evaluate your current equipment, identify performance and security risks, and recommend the most cost-effective path forward.
→ Network Upgrade Services — Planning & Professional Implementation
→ Managed IT Services — 24/7 Support, Monitoring & Strategy
→ IT Assessments — Free Network Environment Evaluation
→ Managed Security — NGFW Deployment & Cybersecurity Monitoring
→ Cloud Migration & Optimization Services
→ Blog: Business Network Components Explained (Deep-Dive Guide)
→ Blog: 3 Ways a Business Network Upgrade Saves You Money


© 2026 All Right Reserved | Ferrara IT